FBI warns ARTEX lets attackers automate intrusions at machine speed
Nov 14, 2026
Cybersecurity
Astrix Security has released the OpenClaw Scanner, a free tool designed to detect deployments of the open-source AI assistant OpenClaw, announced in a press release. The scanner identifies autonomous AI agents operating within enterprise environments, a growing concern as such agents gain capabilities to execute commands, access files, and authenticate to internal systems.
The release follows recent disclosures by researchers highlighting authentication weaknesses in publicly accessible OpenClaw instances. Astrix’s own analysis found similar vulnerabilities in active enterprise environments, including misconfigurations that could allow remote access to devices and sensitive systems such as Salesforce, GitHub, and Slack.
The OpenClaw Scanner operates using read-only endpoint detection and response (EDR) telemetry, running locally without executing commands on endpoints. It is derived from Astrix’s broader security platform and is available as a free download on PyPI to help organizations identify and mitigate AI agent-related risks.
Consider subscribing to one of our newsletters like Cybersecurity AI Weekly, AI Policy Brief or Daily AI Brief.
Also, consider following us on social media:
Weekly report on AI regulations, safety standards, government policies, and compliance requirements worldwide.
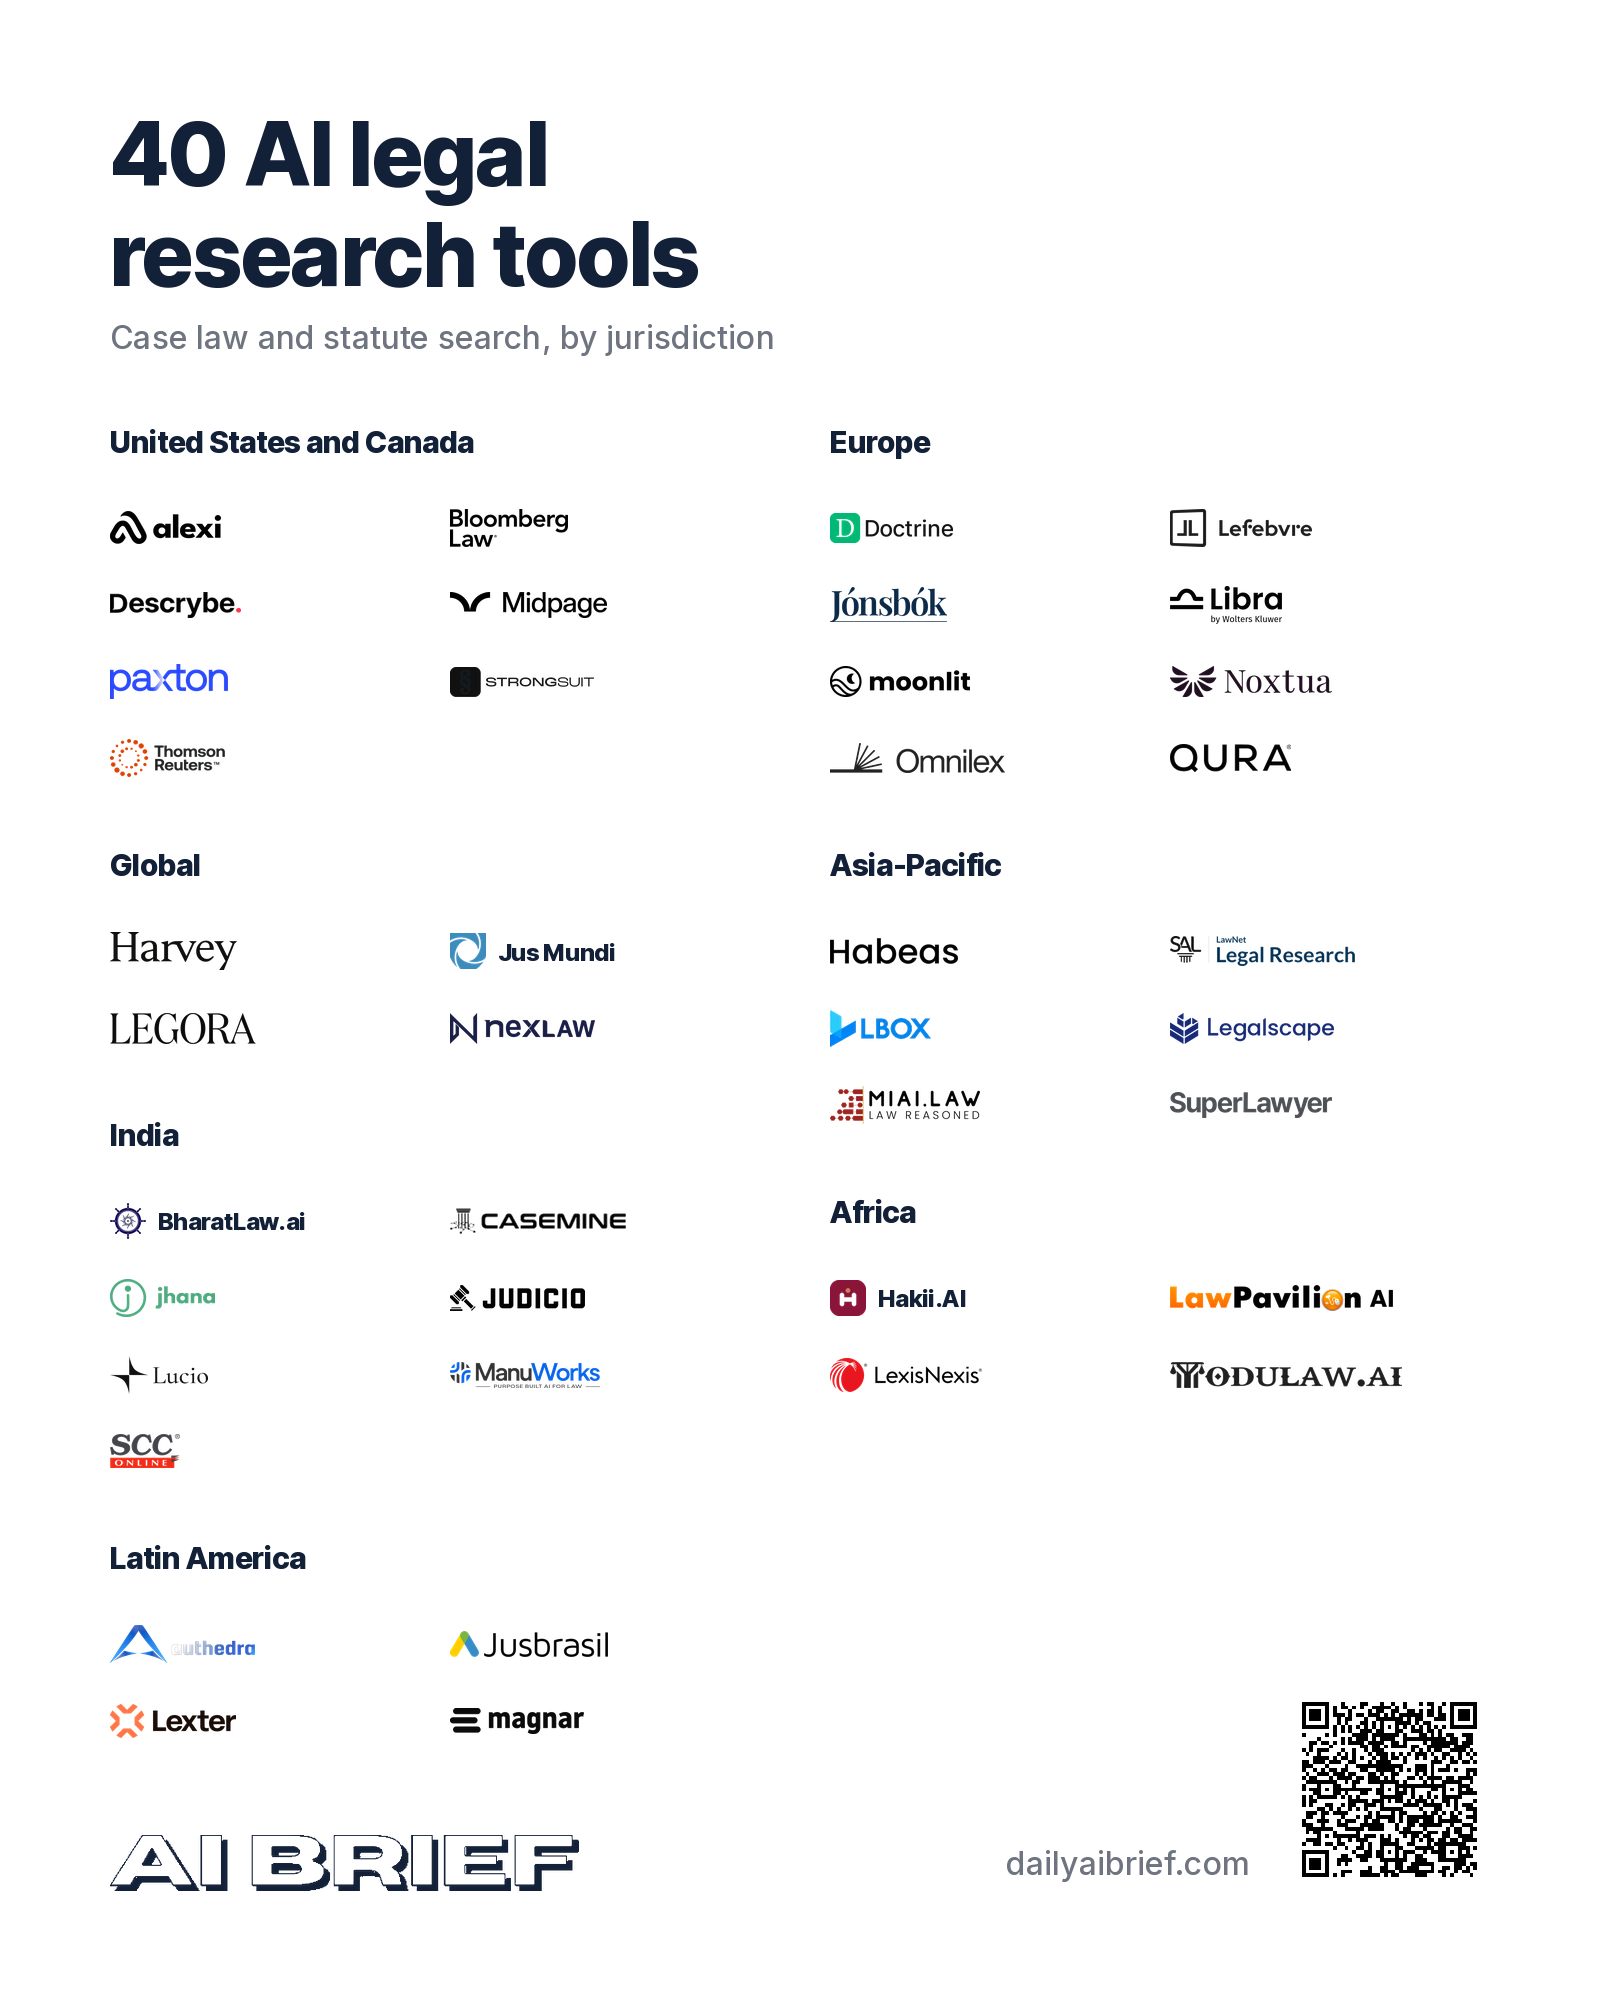
AI products that research case law and legislation for legal professionals.
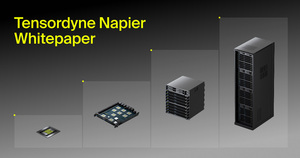
 Tensordyne
This Tensordyne whitepaper presents Napier, an inference-focused AI processor and rack-scale system based on the company’s TDN Math logarithmic number system. It examines infrastructure requirements for large mixture-of-experts and agentic models, compares major inference architecture approaches, and details the TDN AIP processor, TDN72 pod, TDN Link fabric, and Napier Ultra configuration. The paper reports simulation-based performance, cost, and accuracy-validation results, including Tensordyne’s projected comparison of one Napier rack with a nine-rack Nvidia Rubin plus Groq deployment; the chip is reported as taped out and in fabrication.
Read moreDaily AI Brief: the AI news that matters, in your inbox.